Key Highlights
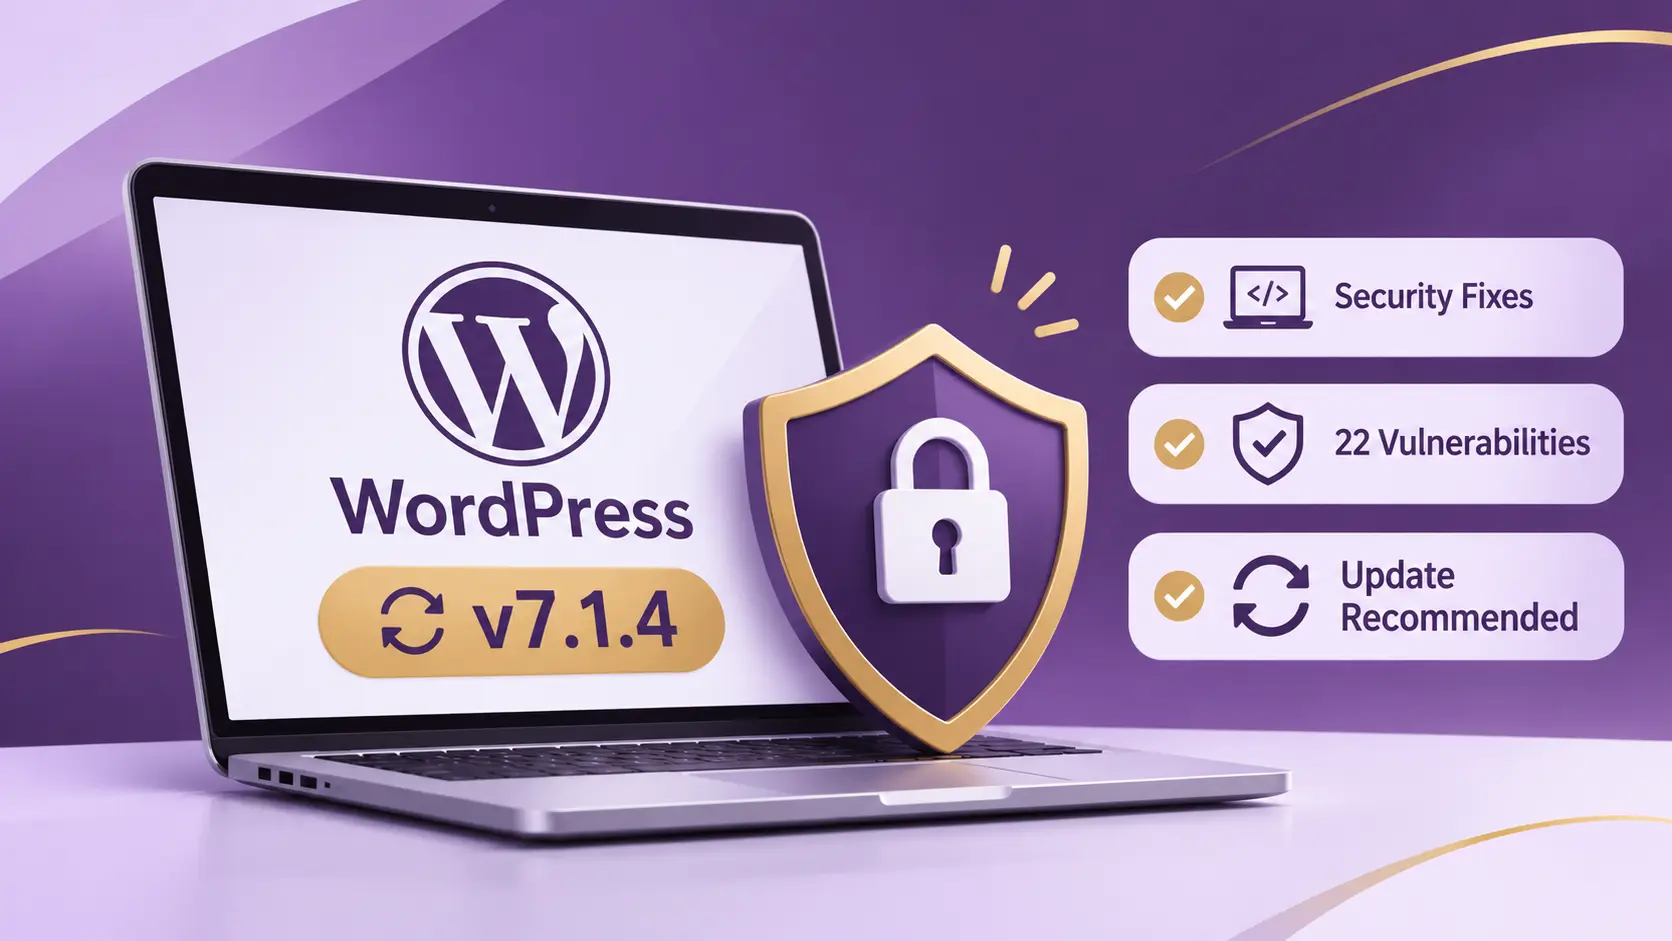
WordPress 7.1.4 fixes 22 security vulnerabilities.
Fixes a potential remote code execution risk in the WordPress update process.
Addresses multiple stored cross site scripting (XSS) vulnerabilities.
Fixes security issues affecting WordPress core, blocks, and admin interfaces.
Website owners should update WordPress and back up their websites before updating.
WordPress has released version 7.1.4 to fix 22 security vulnerabilities affecting its core software. The update addresses several security issues, including a potential remote code execution risk in the WordPress update process.
Key Security Fixes in WordPress 7.1.4
The latest security release includes three major areas of improvement:
Remote Code Execution Risk: Fixes a race condition in the WordPress update process that could potentially allow attackers to execute malicious code on a server.
Stored Cross-Site Scripting (XSS): Addresses multiple vulnerabilities that could affect website security.
Core Security Issues: Fixes vulnerabilities affecting the Interactivity API, blocks, Customizer, and administrative interfaces.
Some of these vulnerabilities affect older WordPress versions, with issues dating back to version 4.7.
Why Should Website Owners Update WordPress?
Outdated WordPress installations can expose websites to security risks. Installing the latest security updates helps protect website data, reduce potential attacks, and keep websites running securely.
Website owners should update to WordPress 7.1.4 if their installations are on an affected version. Before updating, create a complete website backup and check plugin and theme compatibility.
Official Source: WordPress 7.1.4 Security Release
Recommendation: Check your WordPress dashboard and install the security update if it is available for your website.